How to fix "Allocation of JIT memory failed, PCRE JIT will be disabled" warning in Joomla 4
With the release of Joomla 4, they recommend that we upgrade our server's PHP to version 8.
However, PHP versions from 7.2.5 are still accepted, see details at https://downloads.joomla.org/technical-requirements
When using Joomla 4 on PHP 7, you may get an error like "Allocation of JIT memory failed, PCRE JIT will be disabled...", it happens almost throughout the entire page and it looks really confusing.
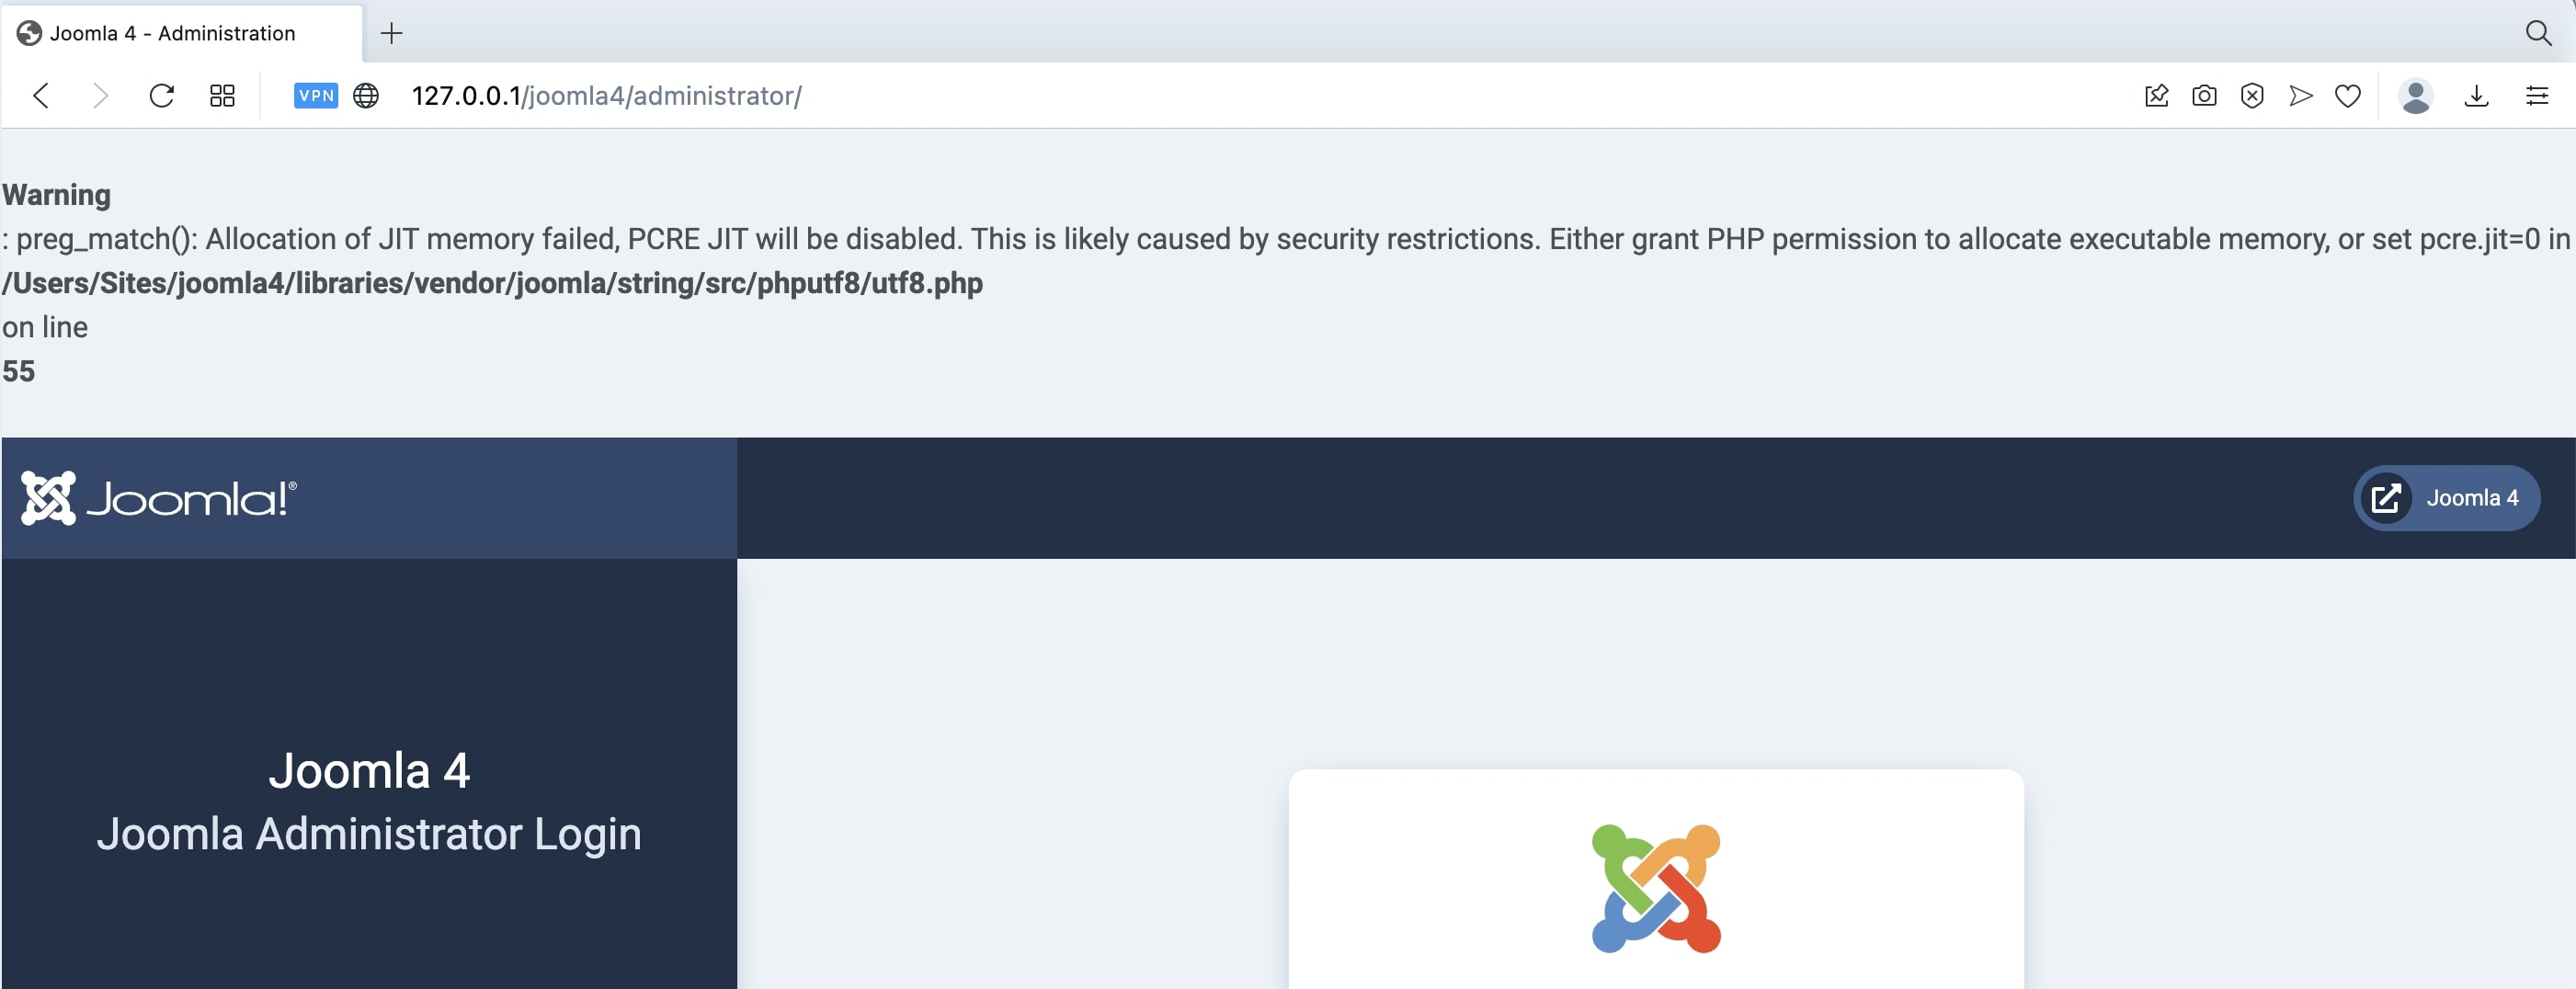
There are ways to fix it:
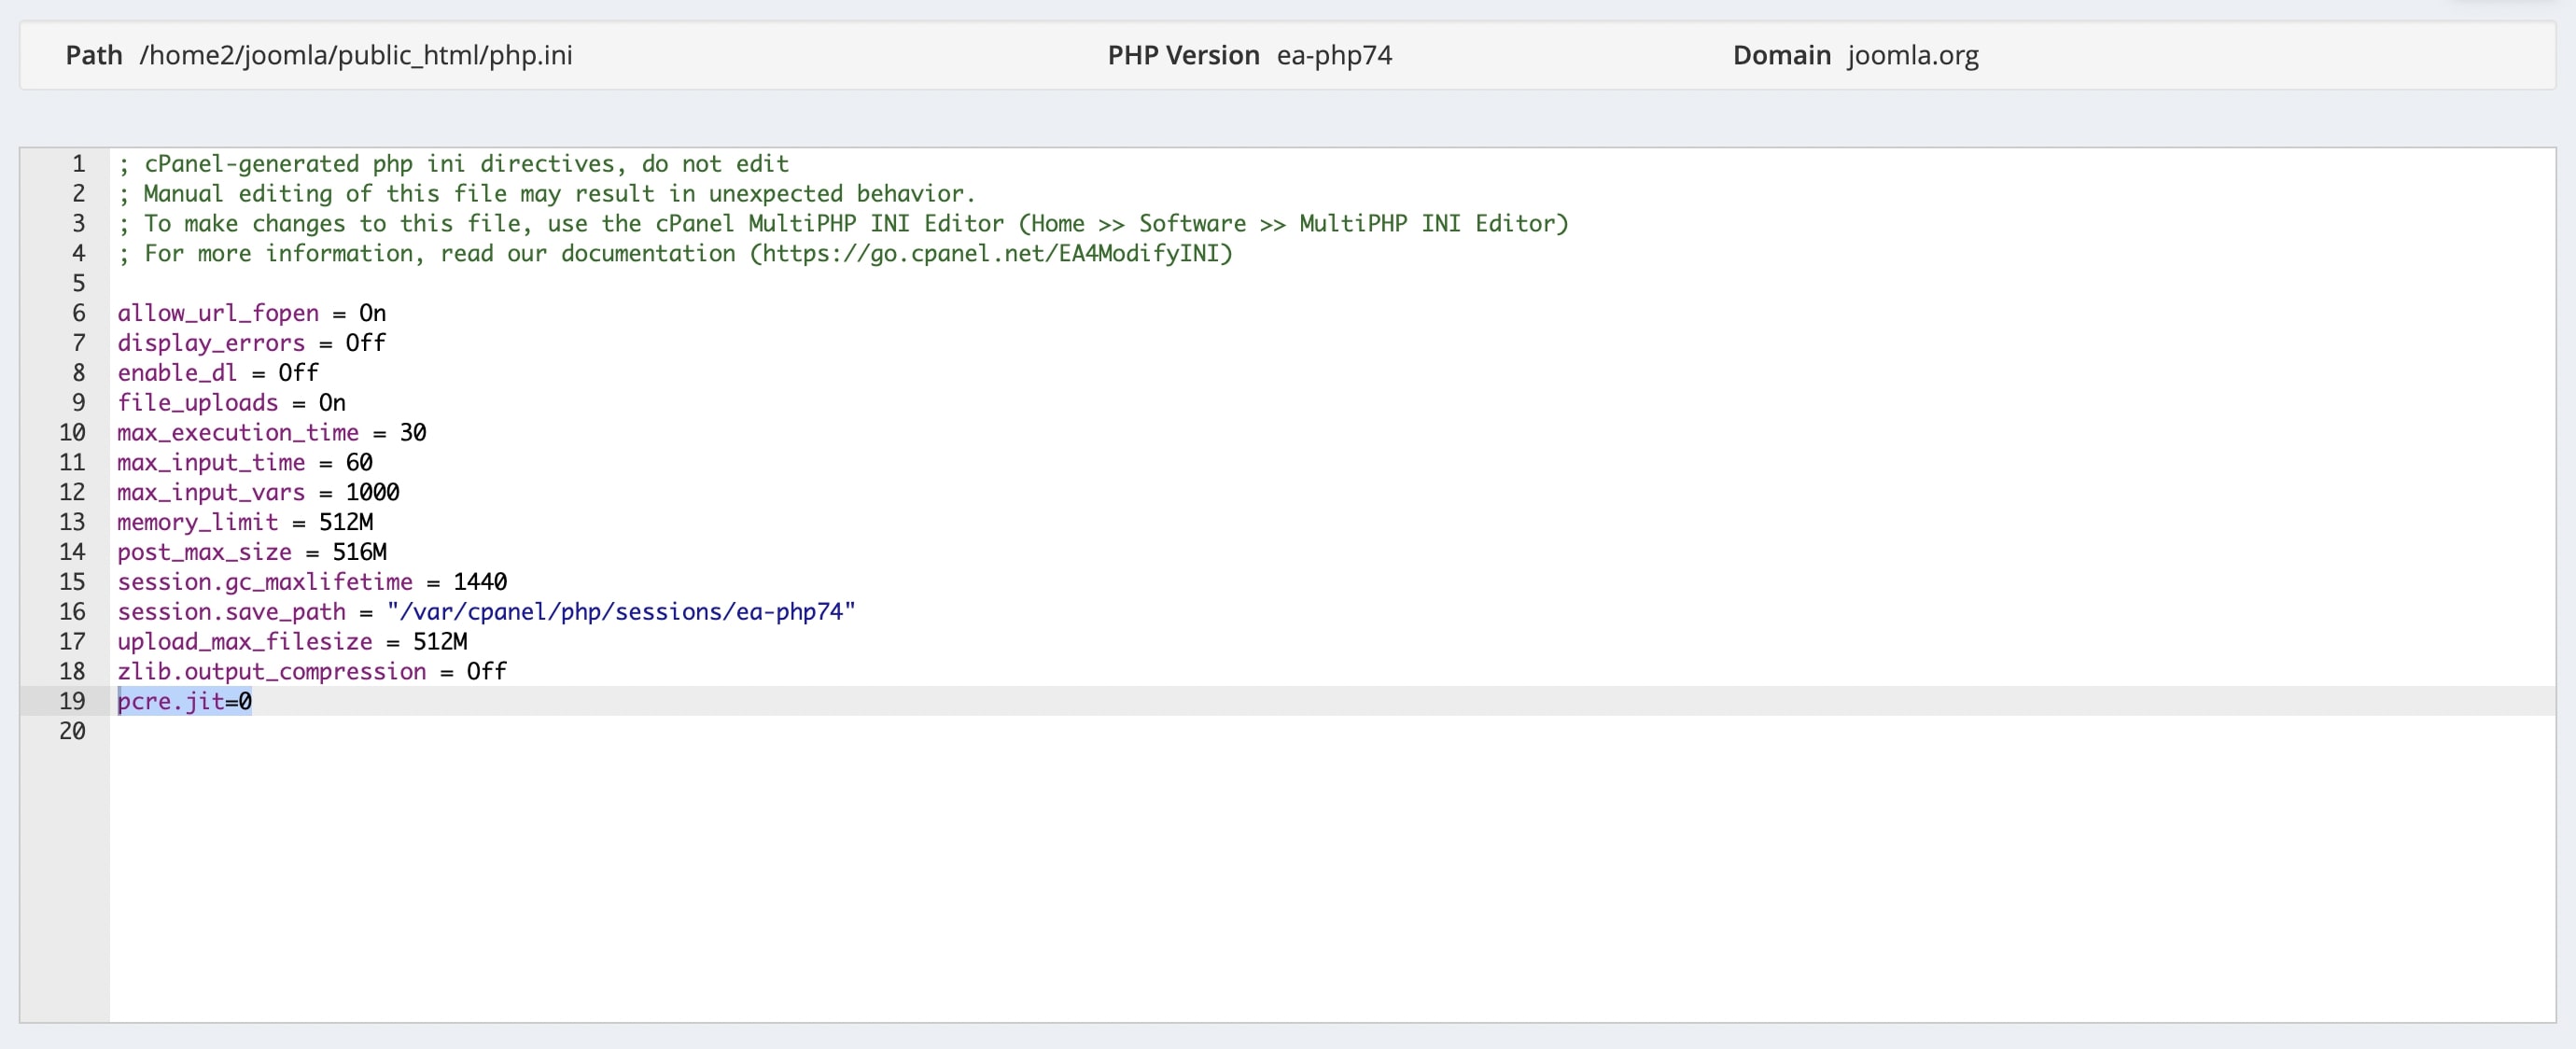
1. Change the settings on the PHP.ini file
Most server/hosting providers support tweaking the basic PHP settings. You can find it from the server/hosting management section.
After opening the PHP.ini file, add the following line of code: pcre.jit=0
Another way is that you can add the above parameter to the JMP PHP Settings extension.
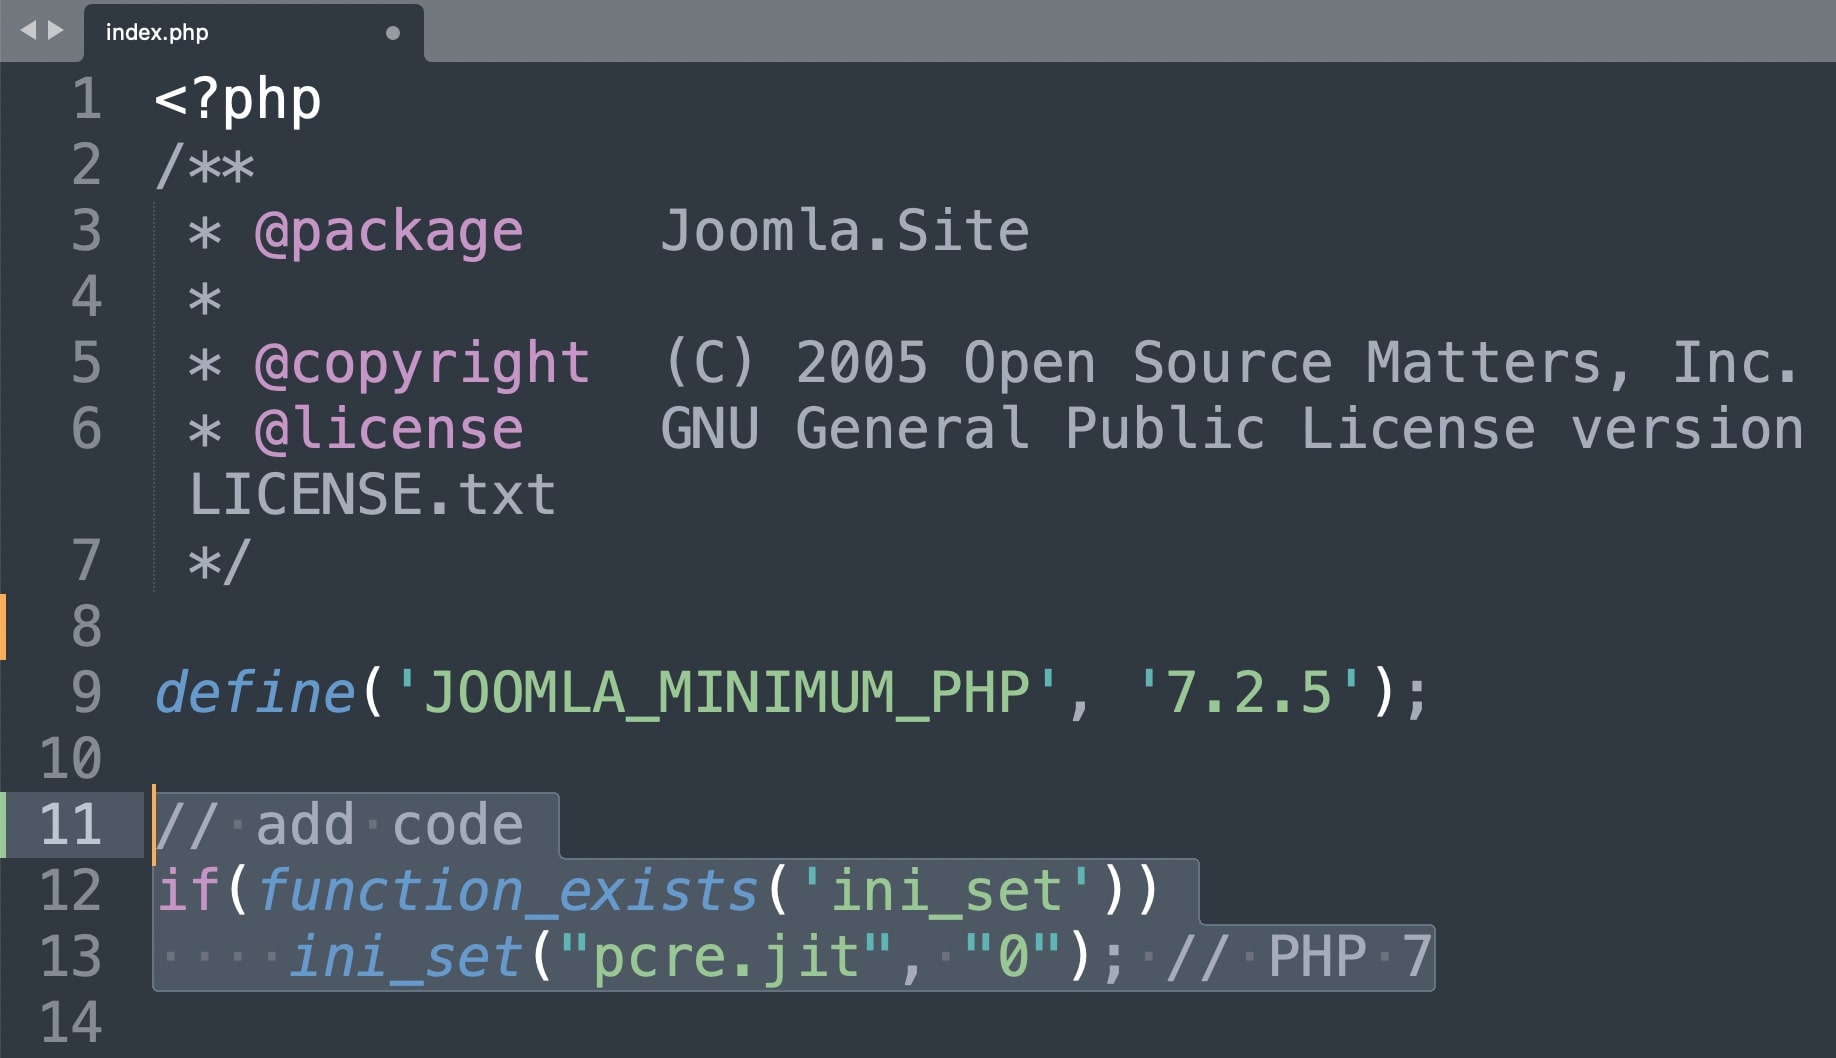
2. Edit the code directly on the index.php file.
All requests on Joomla are made through the index.php file. Please add this line of code:
ini_set("pcre.jit", "0");
... to the files below:
- index.php
- administrator/index.php
3. Change the value of Error Reporting
From the Joomla admin section, go to System > Global Configuration > Server > Error Reporting: None

This is not preferred because you cannot control the error. This may lead to incorrect results.
4. Upgrade to PHP 8.
This is the last way and also the riskiest. It is risky because the extensions you are installing may not be compatible with PHP 8. Of course, if you are installing Joomla for the first time, this is the right thing to do.
I'm considering purchasing your File Attachments extension for a Joomla 5 website.
I intend to use it for distributing 3D CAD model archives (ZIP files) to website visitors.
I have three questions:
1. Does the extension generate temporary download links that automatically expire after a configurable period (e.g. 5 minutes), or are the download URLs permanent?
2. Does it support rate limiting to prevent automated bots from repeatedly requesting downloads?
3. Are the uploaded files stored outside the publicly accessible web directory, and are they delivered through a PHP download controller rather than direct file access?
These features are important because I want to protect the hosting server from automated mass downloads while allowing legitimate visitors unlimited access to different models.
Thank you!
^Add a message editing option for users who cannot use this feature.